

AI Risk in Financial Services: Governance Before Innovation

In financial services, AI risk isn’t only about what might happen. It’s about what you must do — and how quickly — when something does happen. That’s why governance has to come first. Not because innovation is bad, but because the environment is time-bound. When the clock starts, firms need to act decisively with incomplete […]
Claude AI Governance: How to Control a Tool Your Teams Already Use
Claude has moved well beyond a clever chat window. Teams now use it to search the web, work across very large context windows, analyze structured work, and support more agent-like workflows. That shift matters because governance now has to cover more than prompts. It has to cover access, action, evidence, and accountability. Meanwhile, 78% of organizations […]
Shadow AI Is Already Inside Your Organization — The Risk Is Pretending It Isn’t
AI is no longer a future project. It’s a present condition, thanks to shadow AI. Approximately 78% of organizations used AI in 2024, up from 55% the year before. That kind of adoption doesn’t wait for governance. It spreads through daily work — often faster than leadership realizes. And that’s the real issue: the risk isn’t […]
Cybersecurity Readiness Advisory: Managing Elevated Cyber Risk During Global Crises
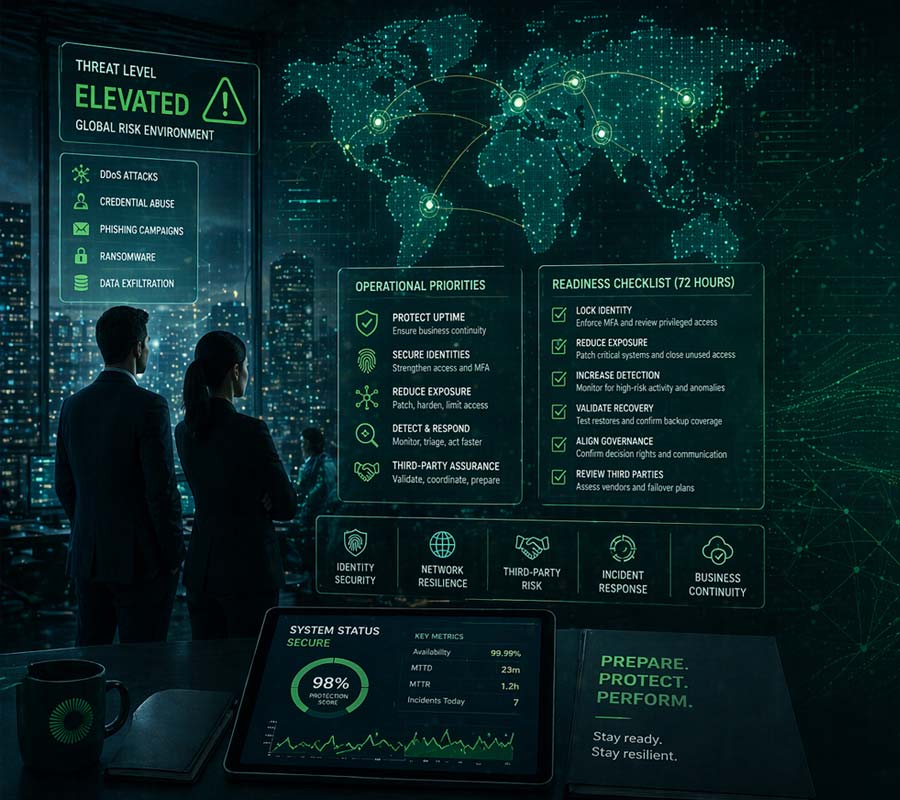
Cybersecurity readiness matters most when the world feels uncertain. During major global events, attackers move fast, because distraction creates opportunity. As a result, many organizations see more noise, more probing, and more “cheap disruption” attempts. Our team prepared this advisory as a practical guide to the operational changes to expect in light of geopolitical tensions […]
Cybersecurity Maturity: Strengthening Resilience in a High-Risk Landscape
Strengthening cybersecurity maturity requires shifting from reactive to proactive resilience. By adopting NIST frameworks and AI-powered monitoring, organizations transform security from a vulnerability into a strategic safeguard that fosters trust and innovation.
When the Clock Starts: Vendor Risk Under Reg S-P
The amended Regulation S-P requires financial firms to assess vendor security incidents within 72 hours. Success depends on clear contracts, updated data inventories, and decisive leadership coordination to manage customer notification obligations effectively.
Reg S-P Readiness Breaks at the Handoff: Mind the Ownership Gaps
Focus on clear ownership and accountability to eliminate regulatory gaps. Reg S-P readiness often falters at the handoff between governance and execution, requiring explicit decision rights and coordinated vendor management to withstand SEC scrutiny.
Exam-Ready vs. Tool-Ready: Can Reg S-P Shift Evidence from Risk to Habit?
Navigating Regulation S-P requires shifting from simply having security tools to maintaining “exam-ready” evidence. High-performing firms treat documentation as a daily habit, ensuring every control is demonstrable, overseen, and defensible under regulatory scrutiny.
Your AI Governance Starter Kit: A CFO’s Checklist for 2026
Over the past year, AI went from a promising concept to something woven into everyday work. It’s also appearing in how bad actors plan and execute attacks. In our December Monthly Intelligence Report, we review how Anthropic uncovered and disrupted the GTG-1002 espionage campaign, where attackers used AI to automate a large share of the intrusion […]
When Your Vendors Use AI: Questions Every CFO Must Ask
Managing vendor AI integration requires shifting from passive trust to strategic oversight. By applying targeted due diligence and 90-day governance plans, CFOs transform third-party exposure into a resilient framework that protects data and financial stability.
CFO’s Ransomware Resilience Dashboard
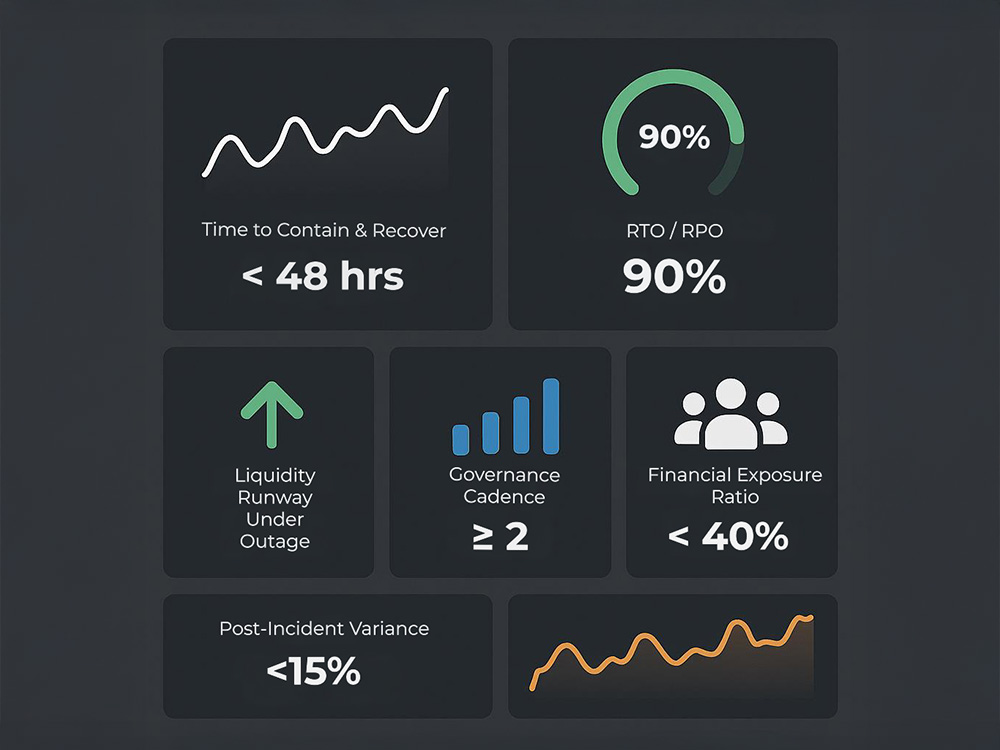
Modernize ransomware defenses by tracking key financial and operational KPIs. Discover how robust detection, recovery alignment, and strategic liquidity planning transform incident response into a vital necessity for business resilience and financial stability.
The CFO’s Ransomware Reality Check
As ransomware threats evolve, CFOs must modernize their financial defenses. Learn how measurable KPIs, robust governance, and strategic recovery frameworks turn digital resilience into a vital business protection for maintaining cash flow.